Who are you, and what can you do?
When you log into your phone, it asks for a PIN, a fingerprint, or a face scan. That’s authentication - the system verifying who you are. Once you’re in, your phone lets you open your apps, but it doesn’t let your friend open your banking app with their fingerprint. That’s access control - the system deciding what you’re allowed to do. These two concepts are the gatekeepers of every secure system.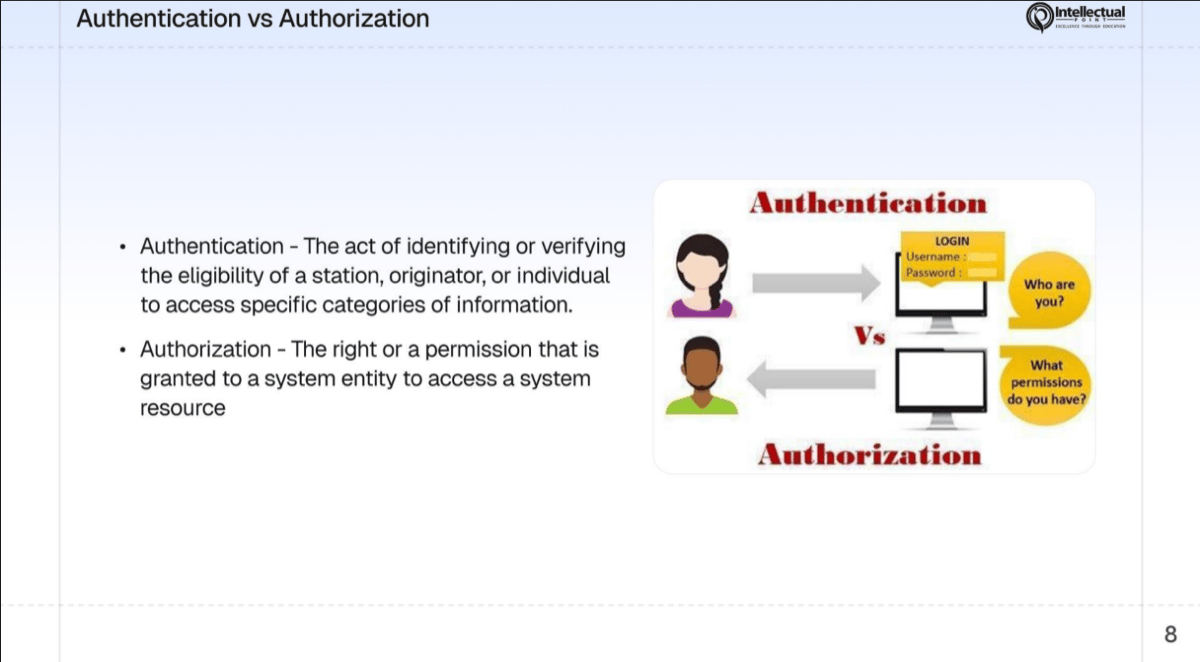
Authentication vs Authorization - who are you vs what can you do
Authentication vs authorization
Three authentication factors
There are three categories of evidence you can use to prove your identity. Each one represents a different factor of authentication.- Something you ARE
- Something you HAVE
- Something you KNOW
- Extremely difficult to forge or steal
- You always have it with you
- Fast and convenient for users
- Can’t be changed if compromised (you can’t get a new fingerprint)
- Can be fooled in some cases (photos tricking facial recognition)
- Privacy concerns - biometric data is highly sensitive
Biometric authentication - something you are
Multi-Factor Authentication (MFA)
Multi-Factor Authentication requires you to prove your identity using two or more different factors. The key word is different - using two passwords (both “something you know”) is not MFA.MFA example
Not MFA
Why passwords alone aren’t enough
Consider these statistics:Access control models
Once you’re authenticated (the system knows who you are), access control determines what you’re allowed to do. There are five major models, each with different rules for how permissions are assigned and enforced. To make these concrete, we’ll use examples from a fictional business you might recognize: Donuts & Dragons - the donut shop from the Cyber Defense Challenge.RBAC - Role-Based Access Control
RBAC - Role-Based Access Control
DAC - Discretionary Access Control
DAC - Discretionary Access Control
MAC - Mandatory Access Control
MAC - Mandatory Access Control
ABAC - Attribute-Based Access Control
ABAC - Attribute-Based Access Control
department=engineering only for users tagged with department=engineering.”RuBAC - Rule-Based Access Control
RuBAC - Rule-Based Access Control
- A router rule that blocks all traffic on port 23 (Telnet)
- A time-based rule that disables Wi-Fi access after business hours
- A content filter that blocks access to social media sites on the company network
Comparison of access control models
Exercise: match the model
For each scenario, identify which access control model is the best fit.1. A hospital gives doctors access to patient records, but nurses can only view vitals and medication schedules
1. A hospital gives doctors access to patient records, but nurses can only view vitals and medication schedules
3. A classified military document can only be accessed by personnel with Top Secret clearance
3. A classified military document can only be accessed by personnel with Top Secret clearance
4. An employee can access the company VPN only between 8 AM and 6 PM, only from a company-issued laptop, and only from within the United States
4. An employee can access the company VPN only between 8 AM and 6 PM, only from a company-issued laptop, and only from within the United States
5. A firewall blocks all inbound traffic on port 22 (SSH) from the public internet
5. A firewall blocks all inbound traffic on port 22 (SSH) from the public internet
6. A retail store's POS system allows cashiers to process sales but only managers can issue refunds over $50
6. A retail store's POS system allows cashiers to process sales but only managers can issue refunds over $50
Key takeaways
Authentication proves identity
MFA combines multiple factors
Authorization determines permissions
Context matters